Continuous security, by AI agents
Break it
before they do.
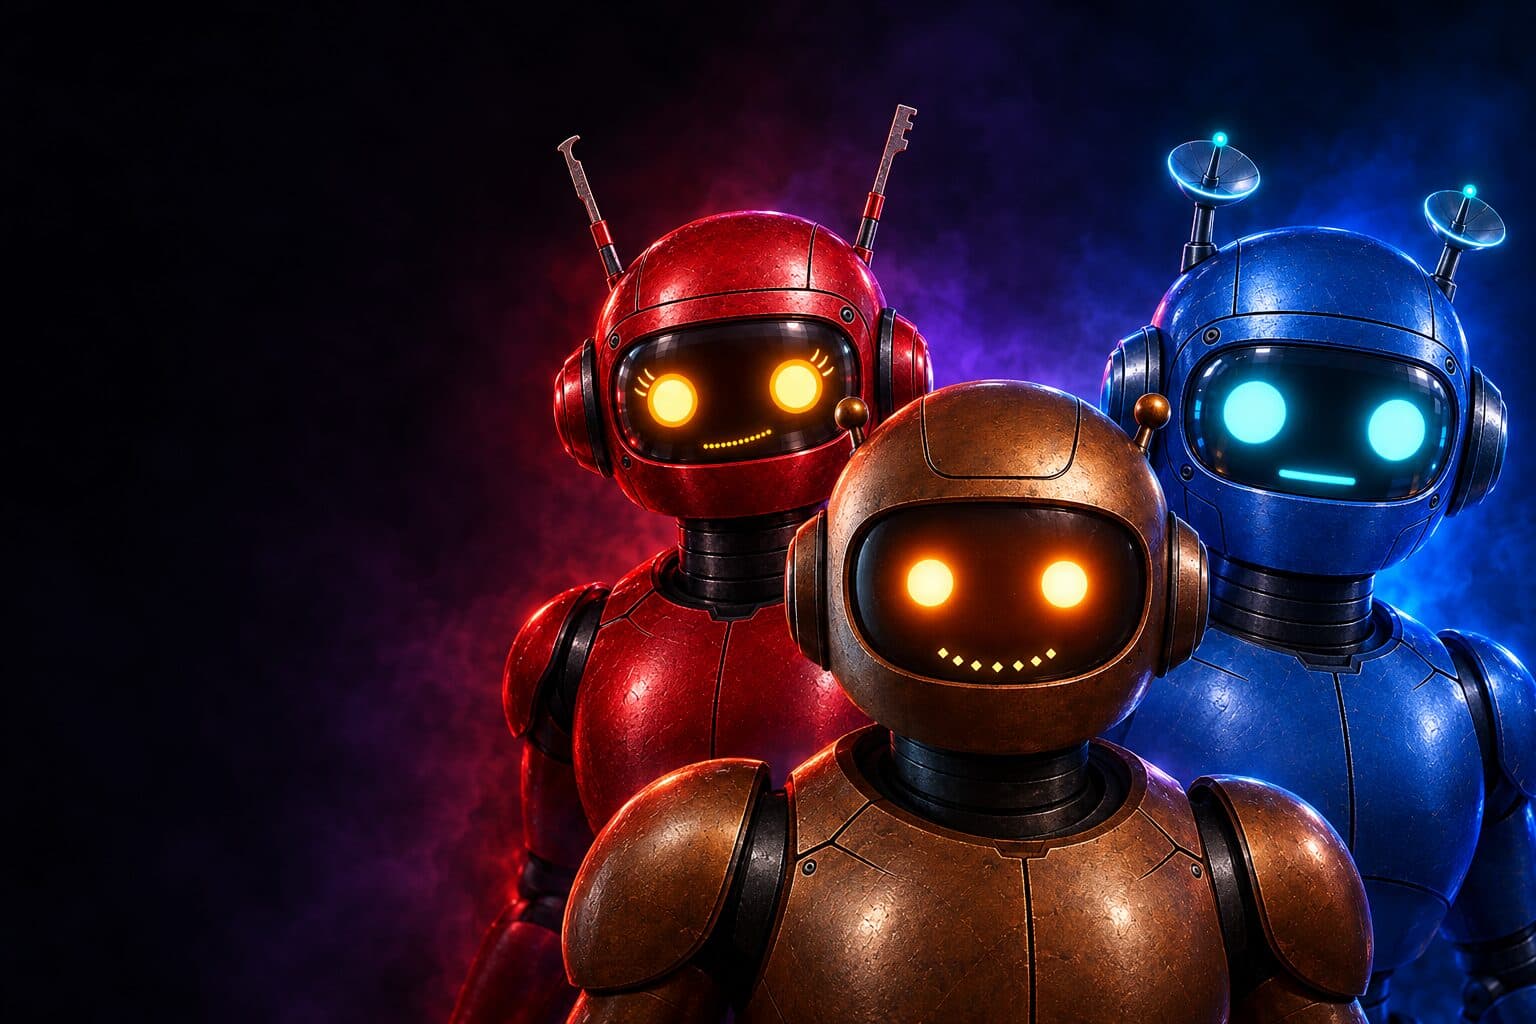
Attackers now use AI to find holes around the clock. So does the KnowAll Purple Team: Pennie attacks, Ollie defends and fixes, and Poppie runs the loop between them.
- new CVEs a day, over the last 30 days
- 566
- added to CISA's exploited list last year
- 245
- agents on watch, around the clock
- 3
No person can read every advisory. The skill is knowing which handful affect your code and are being exploited, and fixing those first.
Sources: NIST National Vulnerability Database (CVEs published in the 30 days to 23 Oct 2026) and CISA's Known Exploited Vulnerabilities catalogue (entries added in 2025).
How it works
Attack. Defend. Fix. Report. Repeat.
A loop that never stops, because neither do the attackers.
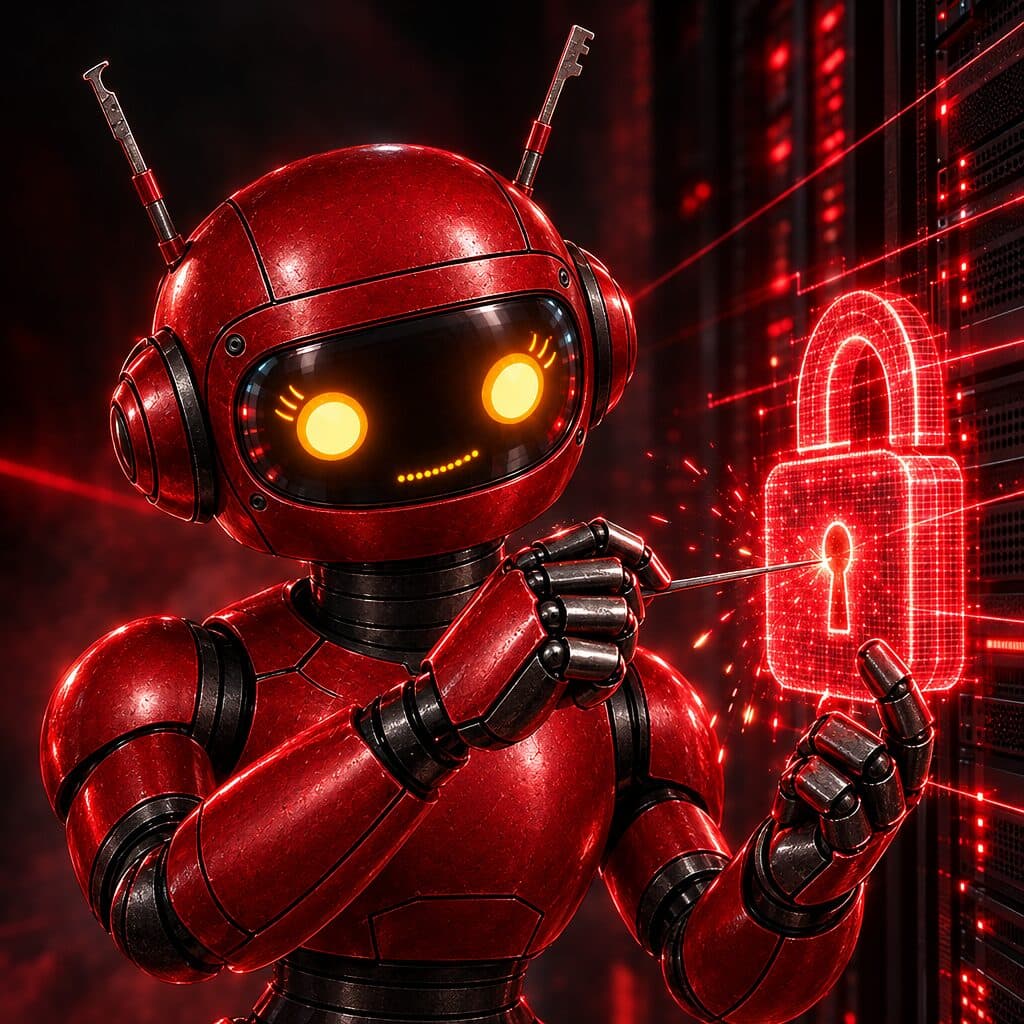
1Pennie attacks
With your written authorisation, Pennie probes your apps, APIs and cloud, and checks every new CVE against your code to prove what is really exploitable.
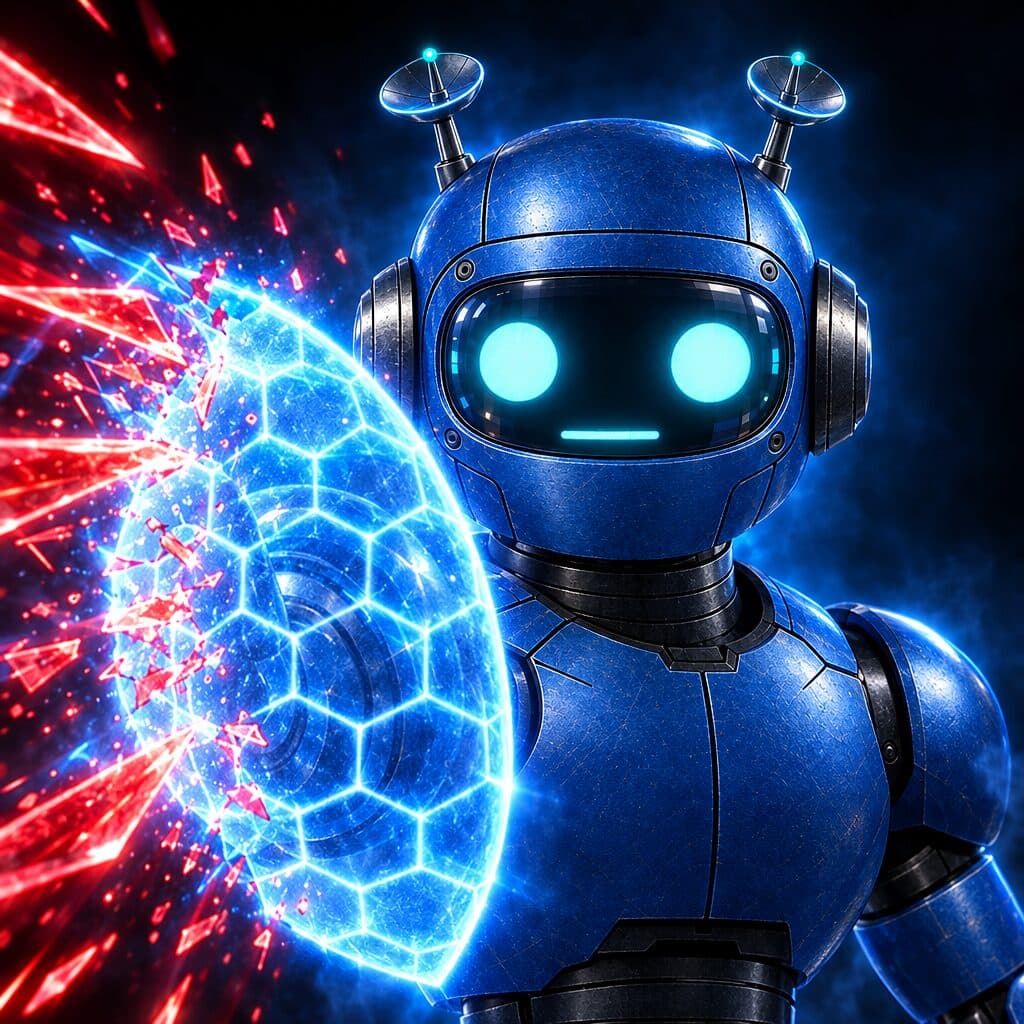
2Ollie defends
Did Ollie see it? He watches your Microsoft Defender for Cloud and Sentinel around the clock, and every attack he missed becomes a new detection.
3Ollie fixes
He opens a pull request with the fix and a test that proves it. Your developers review and merge, then Pennie attacks again to confirm it holds.
4Poppie reports
Poppie scopes the work, tracks every finding as a risk, issue or task, and shows your score, time to detect and time to fix each month.
“Most pen tests end with a PDF. Ours end with merged fixes.”
Meet the team
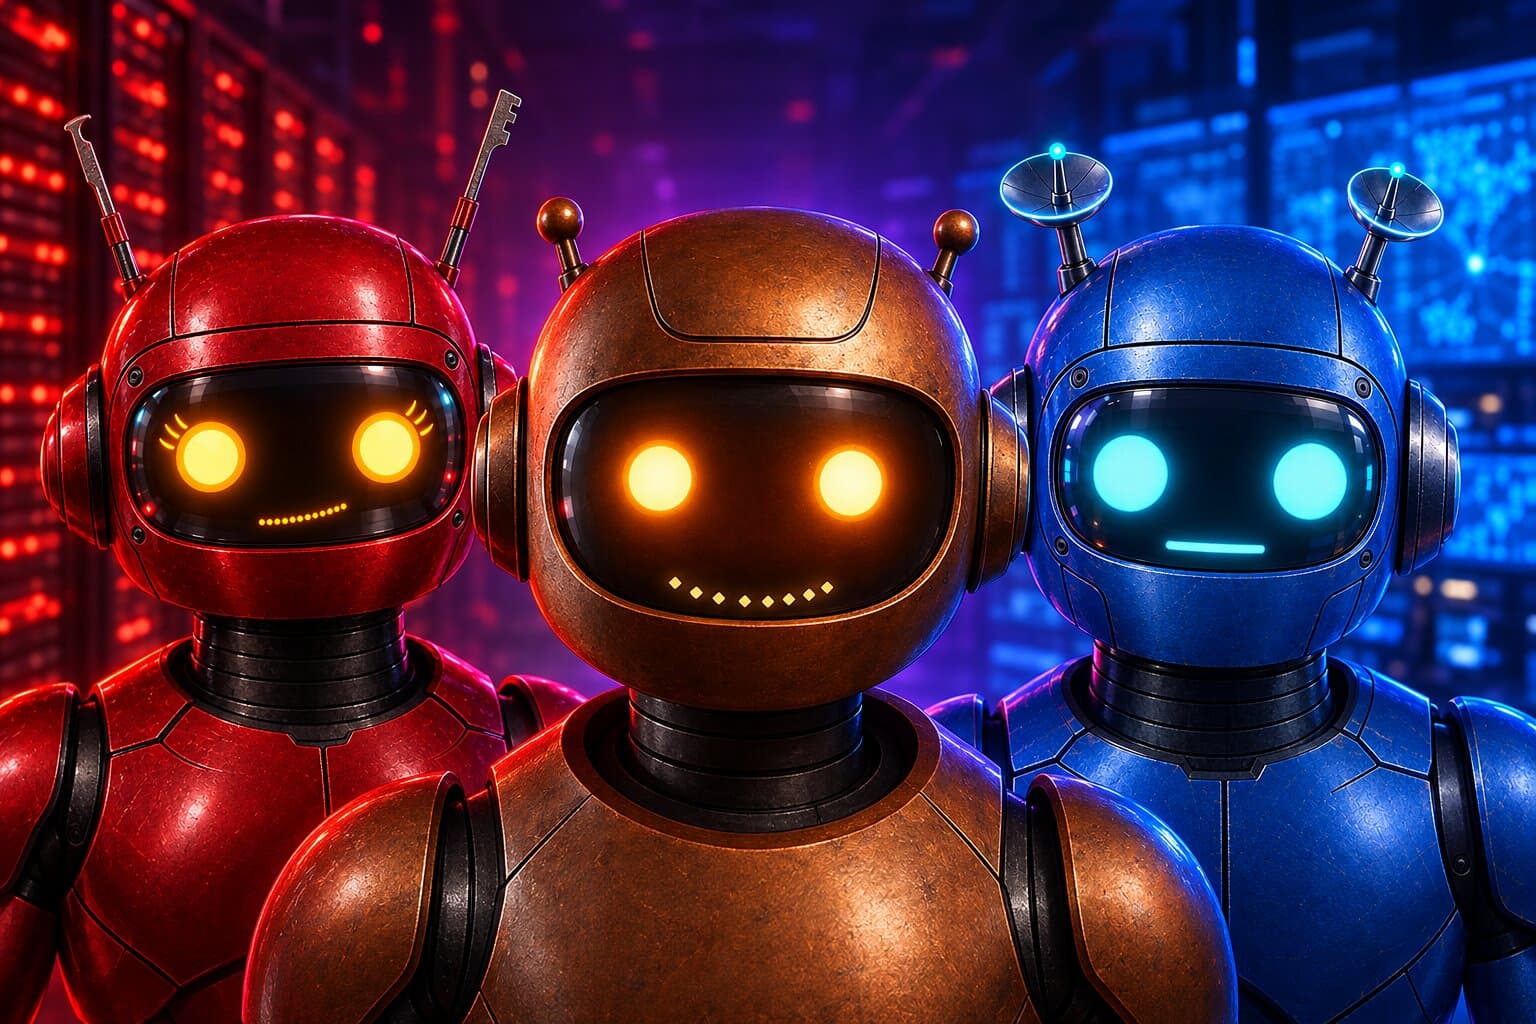
Red attacks. Blue defends. Purple makes them one team.
Pennie the Pen Tester · Red team
Attacks like a real adversary, mapped to the OWASP Top 10, the OWASP LLM Top 10 and MITRE ATT&CK.
Ollie the Operator · Blue team
Filters the daily CVE flood down to what affects you using CISA KEV and EPSS, then defends and patches.
Poppie the Planner · Purple lead
Runs the attack, detect and fix loop between them, so red and blue work as one team.
Works in your GitHub or Azure DevOps, and every change goes through your existing review process.
The numbers
A flood of advisories. A handful that matter.
New CVEs published per year
Source: NIST National Vulnerability Database, counted by publish date via the NVD CVE API 2.0. *1 January to 23 Oct 2026.
| Year | CVEs |
|---|---|
| 2017 | 18113 |
| 2018 | 18154 |
| 2019 | 18938 |
| 2020 | 19222 |
| 2021 | 21950 |
| 2022 | 26431 |
| 2023 | 30949 |
| 2024 | 40704 |
| 2025 | 49972 |
| 2026 (to date) | 88565 |
49,972
new CVEs published in 2025
245
CVEs CISA confirmed as exploited in the wild in 2025. Those are the ones to fix first. Source: CISA's Known Exploited Vulnerabilities catalogue.
What you see each month
Your own Purple Team Portal tracks every advisory that touches your code, what we did about it, and your score over time.
Purple Team Portal
Your security score
+28 in six months
Score by month
Open findings
- Critical0
- High3
- Medium11
- Low24
- Mean time to fix
- 3.2 days
- Attacks detected
- 87%
- Fixes merged
- 46
“I break in so nobody else can.”
Built on the standards
Mapped to the registers your auditors already know.
Every finding carries its public references, so your auditors can trace it, whether for ISO 27001, Cyber Essentials or your own risk register.
CVE & NVD
The public register of known vulnerabilities
CVSS
How severe each one is, 0 to 10
CISA KEV
Which ones attackers are exploiting right now
EPSS
How likely one is to be exploited next
CWE
The type of weakness behind each flaw
Exploit-DB & GHSA
Public exploits and open-source advisories
OWASP Top 10
The most critical web-app risks
OWASP LLM Top 10
Prompt injection and other AI-app risks
MITRE ATT&CK
The catalogue of real attacker techniques
Works with what you already run
Nothing new to install: the team works inside your code hosting, security tools and Microsoft tenant, and bills as hours on a KnowAll support plan (CISP), new or existing.
Code and delivery
GitHub
repos, issues, pull requests, security advisories
Azure DevOps
repos, pipelines, Boards work items
Dependabot and Renovate
routine dependency upgrades
CodeRabbit
AI review on each fix, in repos where you use it
Security scanning
GitHub Advanced Security
code, secret and dependency scanning, on GitHub or Azure DevOps
ZAP (Zed Attack Proxy)
non-destructive web app scans
Nuclei
checks for known CVEs on your public sites
Microsoft security
Microsoft Defender for Cloud
posture, Secure Score, workload alerts
Microsoft Sentinel
detections Ollie adds after each test
Azure Lighthouse
delegated, revocable access to your Azure
Identity and access
Microsoft Entra ID
your sign-in; agents as named guests or agent identities you can switch off
AI models
Microsoft Foundry
OpenAI and Claude models, optionally in your own Azure tenant
Time and billing
Thyme and Business Central
agents log the real hours they work to your support plan
FAQ
Questions
Get started
See how the Purple Team would work for you
Tell us a little about your setup. We'll come back with a scoped plan: what Pennie would test, what Ollie would watch, and what your first month's report would show.
- GitHub or Azure DevOps
- Nothing is tested without written authorisation
- Every fix goes through your existing review process
Want the full picture first? View the Purple Team presentation.
Or just email us at hello@knowall.ai.